Proxmox Backup Server has its own users, API tokens and permissions, separate from Proxmox VE. Aprox lets you manage all of them from your device: add users, set passwords, unlock two-factor sign-in, create API tokens for Proxmox VE or sync jobs, and grant or remove permissions. Roles and realms are listed for reference. Viewing the lists is free. Opening a user to edit it, and every change, need Aprox Pro.
Where to find it
Sidebar › your Backup Server › Access Control.
A picker at the top switches between Users, Permissions, Roles and Realms.
Users
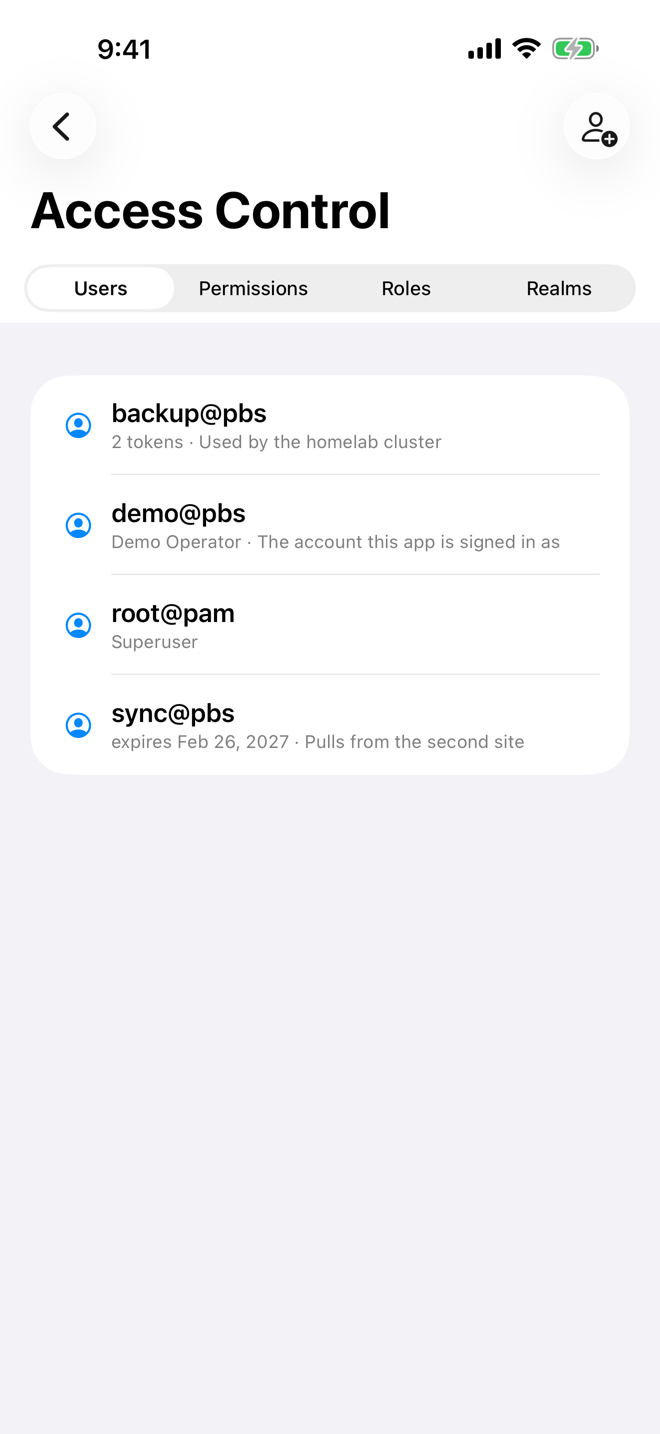
The Users list shows every user with their name, the number of API tokens, and notes such as disabled or the expiry date. Your own account is marked you. A user locked out of two-factor sign-in carries an orange lock sign (Two-factor locked).
Add a user
Needs Aprox Pro.
Tap Add User. The New User sheet opens.
Fill in the fields:
Field What to enter User name The login name, without the realm, for example backup-admin.Realm Where the user signs in, for example pbs(Backup Server's own users) orpam(Linux users of the server).Password (at least 8 characters) Only for the pbsrealm. Users of other realms sign in with the password their realm knows.Enabled On by default. Turn it off to block sign-in without deleting the user. Expires / Expiry Turn on Expires and pick the Expiry date after which the account stops working. Details Optional First Name, Last Name, E-Mail and Comment. Tap Save.
A new user has no permissions. Add some under Permissions (see below).
Edit a user
Needs Aprox Pro.
- Tap the user. The Edit User sheet opens.
- Change Enabled, Expires / Expiry or the Details.
- Tap Save, or Close to leave without changes.
You cannot disable, set an expiry for, or delete your own account or root@pam. That keeps you from locking yourself out.
Set a password
For users of the pbs realm only. Needs Aprox Pro.
- Open the user.
- Under Password, enter the New password (at least 8 characters).
- Tap Set Password. Aprox shows Password changed.
Unlock two-factor sign-in
When someone enters too many wrong two-factor codes, Backup Server locks their two-factor sign-in. Needs Aprox Pro.
- Open the user marked Two-factor locked.
- Read the note "Too many wrong codes locked this user's two-factor sign-in."
- Tap Unlock Two-Factor. Aprox shows Two-factor unlocked.
Delete a user
Needs Aprox Pro.
- Open the user.
- Tap Delete User….
- Confirm "Delete <user>?" with Delete User.
Its API tokens and every permission that names it are removed too. Backups it owns stay.
API tokens
API tokens let programs sign in without a password: a Proxmox VE cluster that backs up to this server, a sync job on another Backup Server, or Aprox itself. Tokens belong to a user and are managed inside that user. A token acts for its user, limited to the permissions given to the token itself.
Create a token
Needs Aprox Pro.
- Open the user.
- Under API Tokens, tap Add Token. The New Token sheet opens.
- Enter the Token name, for example
pve. The full Token ID becomesuser@realm!pve. - Optional: set Enabled, Expires / Expiry and a Comment.
- Tap Create.
- The Token Secret screen shows the Token ID and the Secret. Tap Copy Secret (it confirms Copied) and store the secret safely.
- Tap Done.
Important
Copy the secret now. Backup Server never shows it again. If you lose it, regenerate it.
A new token has no permissions until you give it some. Add a permission for the token under Permissions (see below).
Edit, regenerate or delete a token
Open the user. Each token in its API Tokens list shows its name, comment, expiry and whether it is disabled, plus a menu button with these actions. All need Aprox Pro.
| Action | What happens |
|---|---|
| Edit… | Change Enabled, the expiry and the comment in the Edit Token sheet, then tap Save. |
| Regenerate Secret… | Confirm "Regenerate the secret of <token>?" with Regenerate. Whatever uses the current secret stops working immediately. The Token Secret screen then shows the new secret once; tap Copy Secret. |
| Delete… | Confirm "Delete token <token>?" with Delete Token. Whatever uses it stops working immediately, and its permissions are removed. |
To sign in to this Backup Server in Aprox with a token, see Create an API token.
Permissions
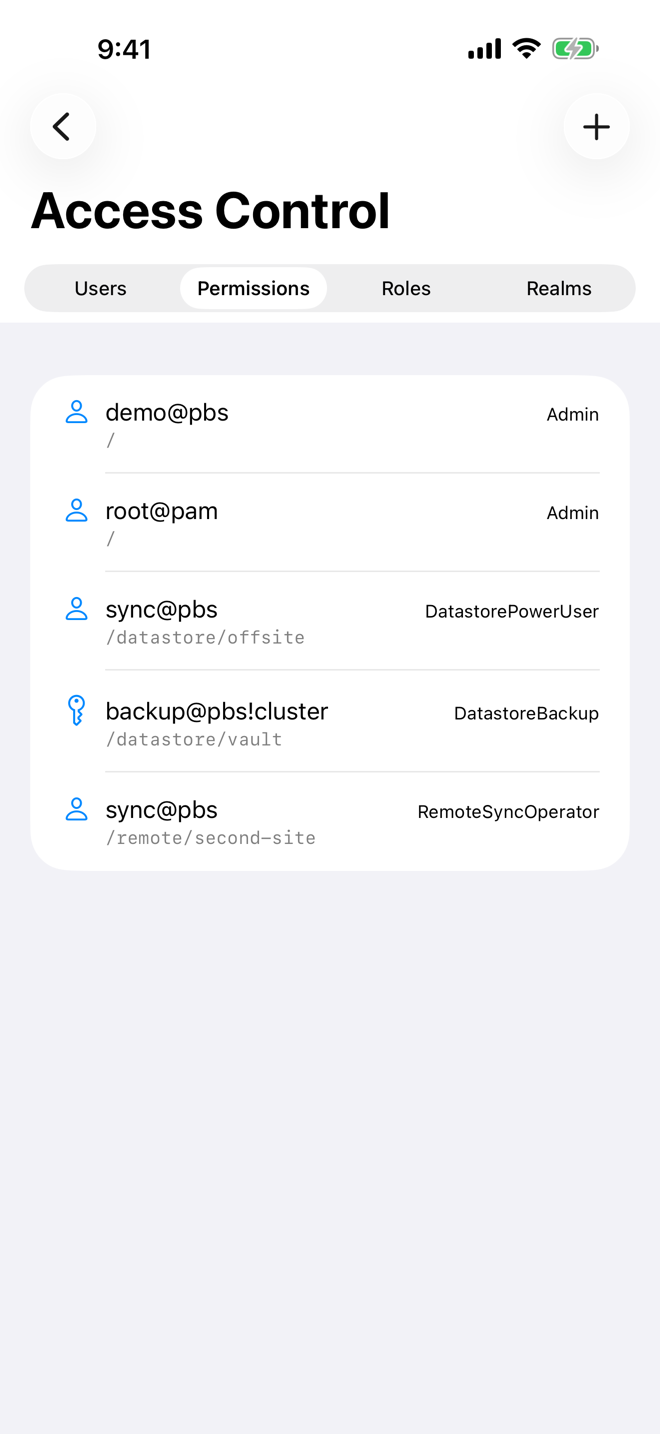
A permission gives a user, group or token a role on a path. The Permissions list shows each entry with its user, group or token, its path and its role. A path marked (this path only) does not apply below it. If nothing is set, the list reads "No permissions are set. Only root@pam can use this server."
Add a permission
Needs Aprox Pro.
- Choose Permissions in the picker.
- Tap Add Permission.
- Choose the Path, for example
/datastore/backupfor one datastore or/for the whole server. Or type it under Or type a path. - Leave Applies below this path on to include everything under the path, for example all namespaces of a datastore.
- Choose who gets the permission:
- For a user or token, pick it under User or Token. If the list is empty, type it as
user@realmoruser@realm!token. - For a group, turn on Group and type the group name.
- For a user or token, pick it under User or Token. If the list is empty, type it as
- Choose the Role, for example
DatastoreBackupfor a Proxmox VE cluster that writes backups, orDatastoreReaderfor read access. The role's description appears below the picker. - Tap Add.
Remove a permission
Needs Aprox Pro.
- In the Permissions list, swipe the entry and tap Remove, or long-press or right-click it and choose Remove….
- Confirm "Remove <role> for <user> on <path>?" with Remove Permission.
Roles and realms
These lists are read-only.
- Roles: each role with its description and the privileges it grants. Use it to choose the right role for a permission.
- Realms: each authentication realm, such as
pamorpbs, with its type and comment.
Requirements on the server
Changing users, tokens and permissions typically needs Permissions.Modify. If a right is missing, Aprox explains what was refused.
Good to know
- These are Backup Server users only. Proxmox VE users and permissions are managed in the Proxmox VE web UI.
- A Proxmox VE cluster that writes backups to this server usually signs in with an API token that has the role
DatastoreBackupon the datastore.